> ## Documentation Index
> Fetch the complete documentation index at: https://docs.pullfrog.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Permissions
> Who can see and change what in Pullfrog, based on each person's GitHub role.
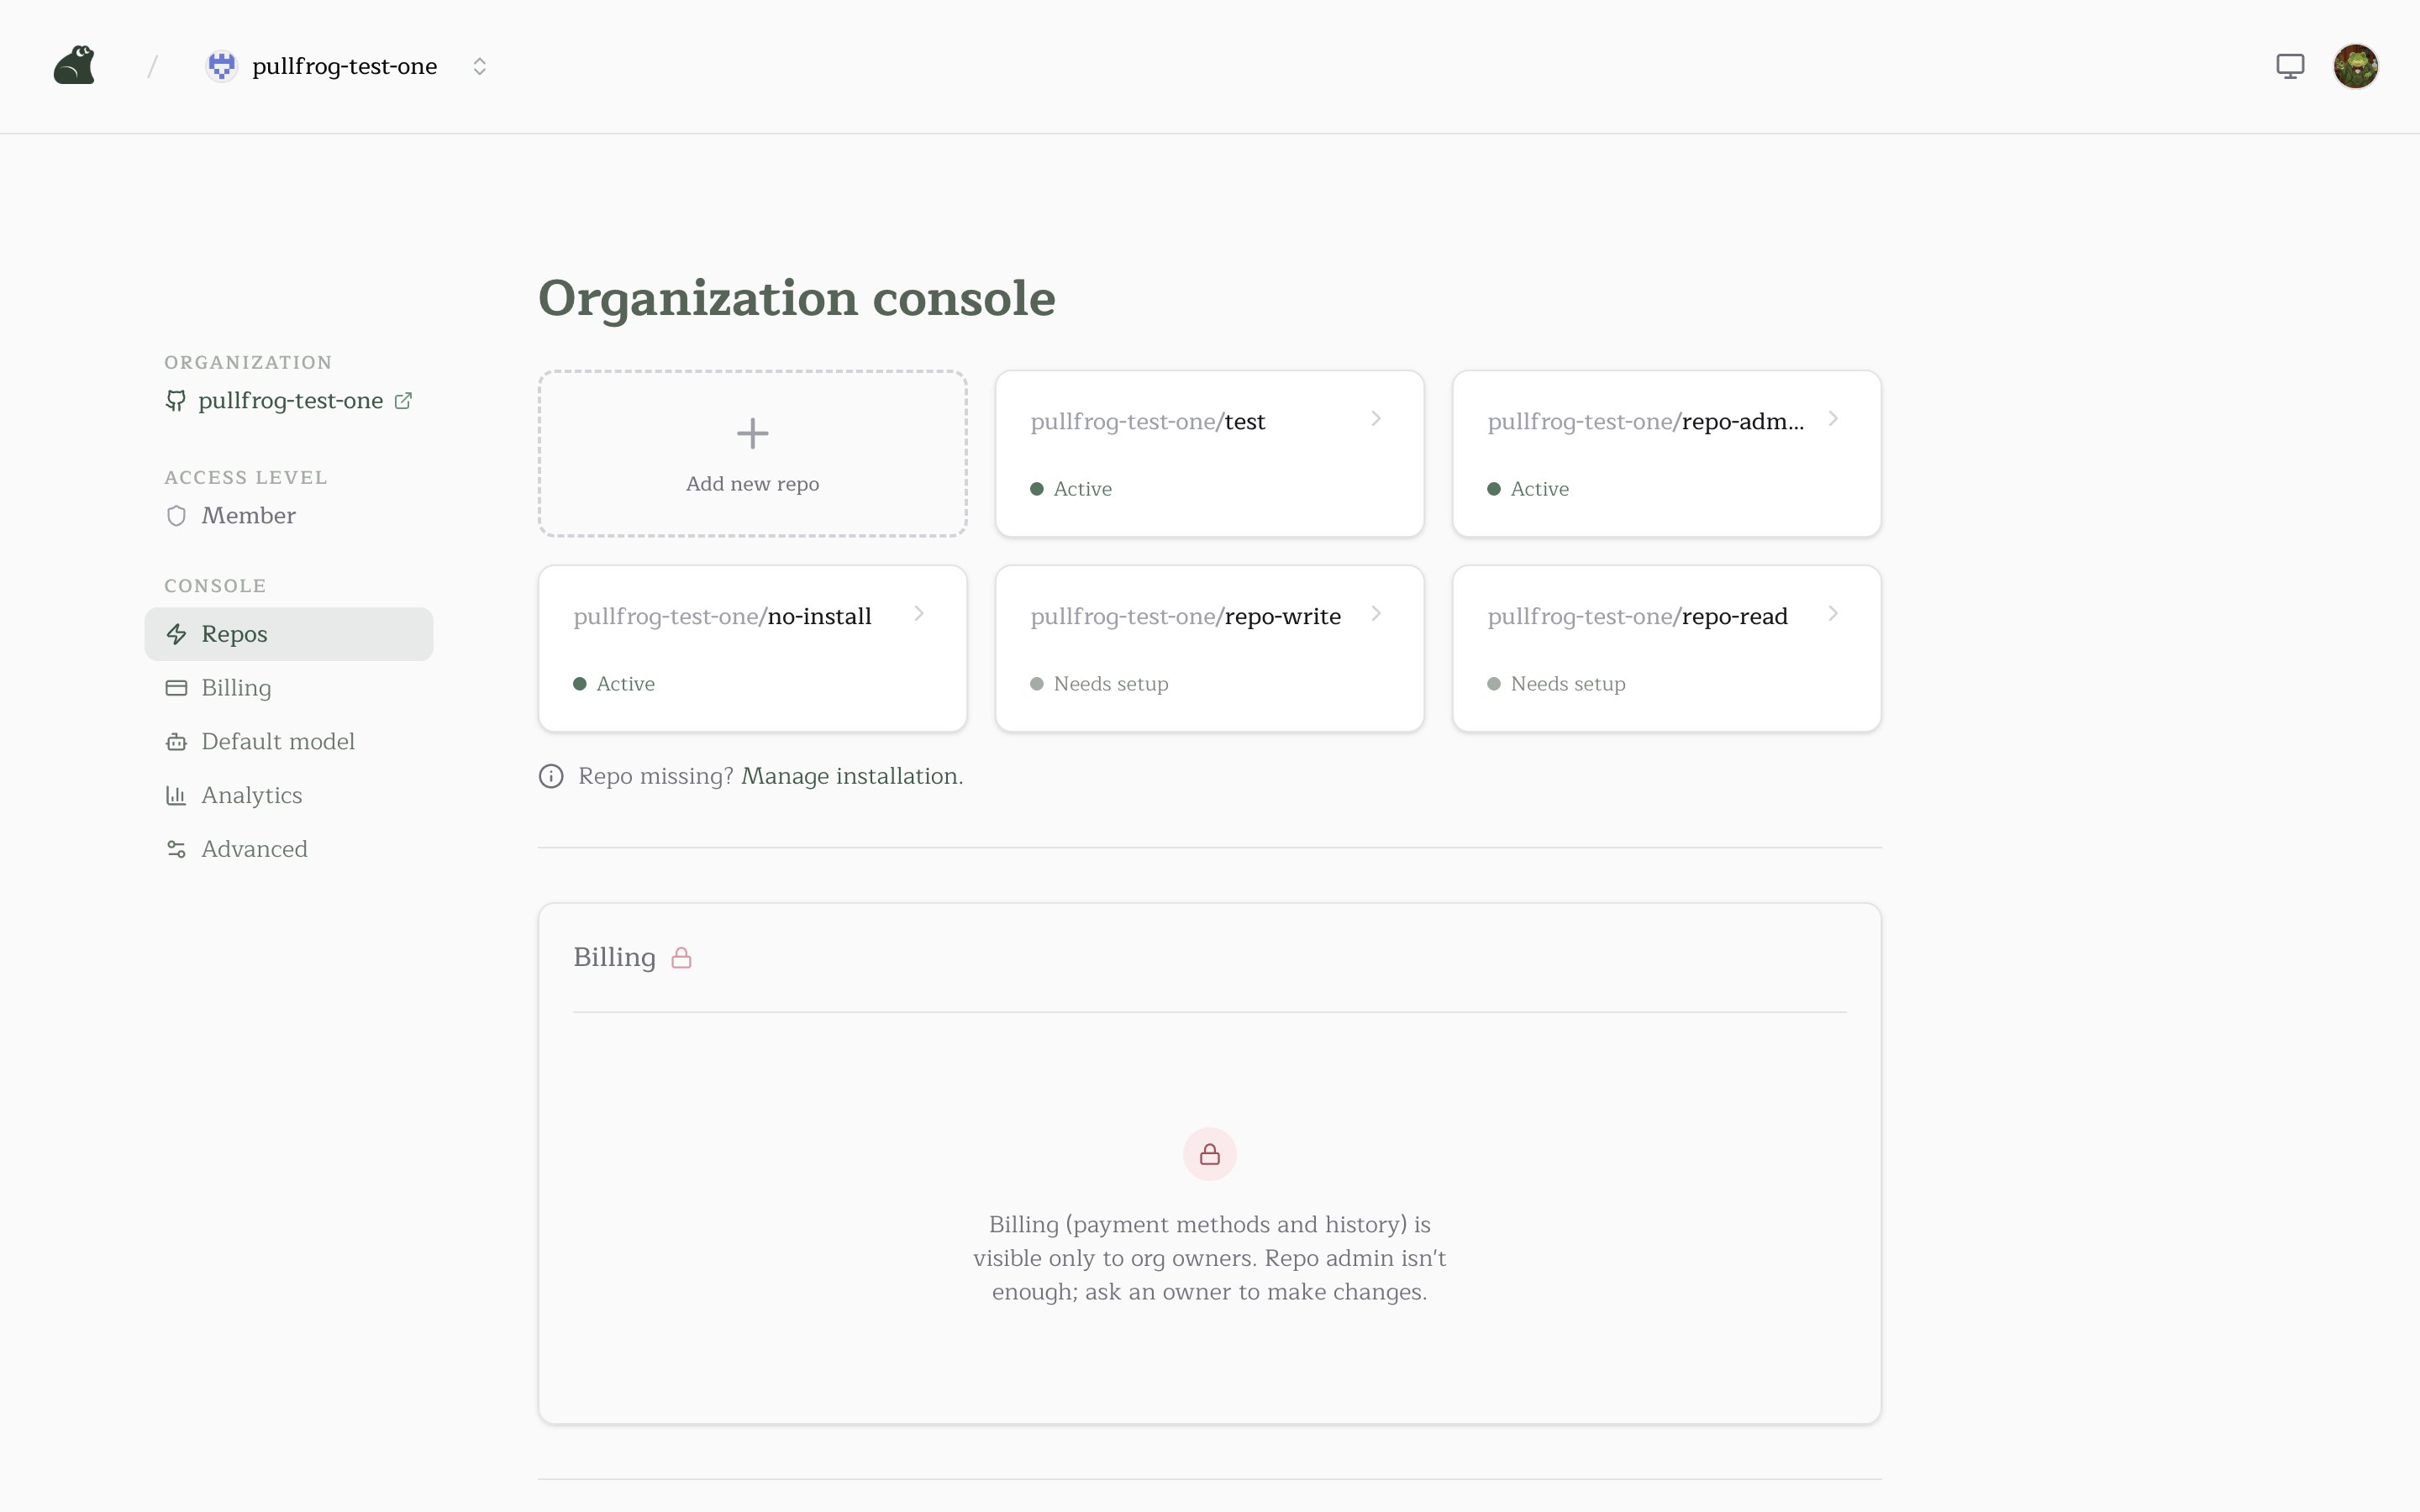
Pullfrog takes every permission from GitHub. There is no user list, invite step or seat to manage: a teammate signs in with GitHub and sees the organizations and repositories they can already reach.
 ## Roles
| GitHub role | What it allows in Pullfrog |
| - | - |
| Repo read | Open the repo console and view active and past runs. |
| Repo write | Trigger runs from the console prompt box. Set the repo up. Edit the **Model**, **Hooks**, **Comments**, **Standing instructions**, **Learnings** and **Flags** cards and every automation. Disable and re-enable Pullfrog on the repo. |
| Repo admin | Edit the **Security** card (code pushes, signed commits, shell isolation, environment allowlist) and the **Secrets** card. Turn on **Auto-merge approved PRs** and Pullfrog for OSS. |
| Outside collaborator | See only the repos they collaborate on in the organization console, with no organization-wide cards. Their repo role applies in each repo console. |
| Org member | Edit the organization **Default model** card and, under **Advanced**, **Standing instructions**, **Cross-repo brief**, **Cross-repo learnings** and **Flags**. View **Analytics** on a paid plan. |
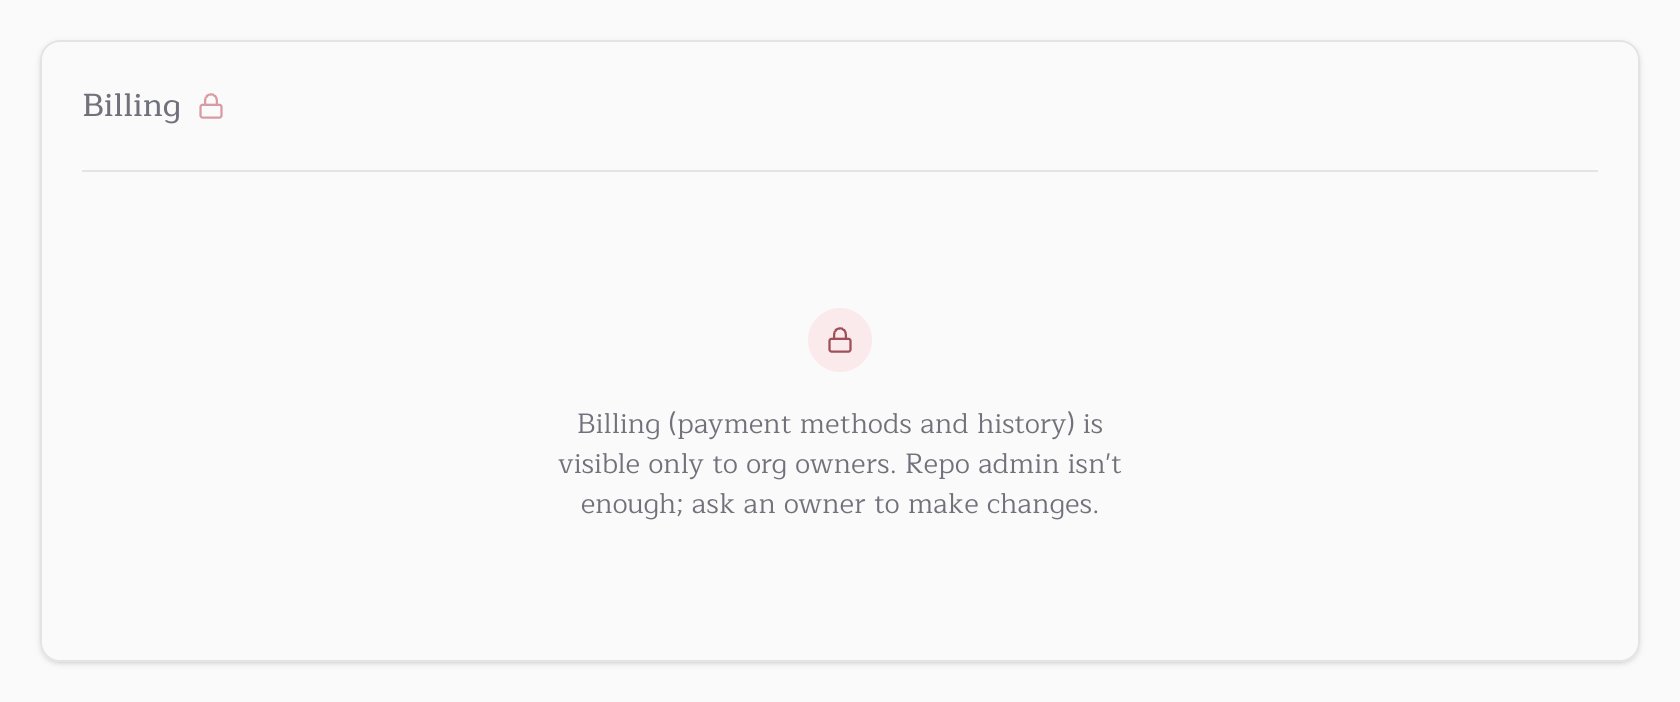
| Org owner | Manage **Plan and payment**, **Providers** and **Secrets**: the plan, payment method, Pullfrog Router credit, and account-level provider keys and secrets. View the billing and Router history pages. |
Each repo role includes the ones above it, so an admin can do everything a write user can. Organization roles are separate from repo roles: an org member still needs write access to change a repo's settings. On a personal account, the account owner holds every role.
## Notes
* **Repo setup.** Adding `pullfrog.yml` needs write access to that repo, not an organization role. The commit is made as you; if the default branch is protected, Pullfrog opens a pull request from `pullfrog[bot]` instead. A private repository in an organization still needs a [plan](/billing) that covers it.
* **Locked cards.** A card you cannot edit stays in place with a lock icon and a short message naming who can change it, so links into the console still resolve. The API enforces the same rules, so billing data never reaches a non-owner's browser.
 * **Organization-wide reach.** Organization standing instructions and flags apply to every run in every repository of the organization, including [flags](/flags) that set the model or timeout. Any org member can edit them; outside collaborators cannot.
* **Org owners.** Pullfrog reads the owner role from GitHub again before billing changes instead of trusting a cached value. GitHub's API calls this role `admin`.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.